In a significant regulatory shift aimed at curbing the relentless surge of spam and fraudulent communication, the Telecom Regulatory Authority of India (TRAI) has mandated that caller-ID and call-management applications share their user-generated spam reports directly with telecom operators. This directive, issued this past Friday, marks a pivotal moment in the governance of India’s digital telecommunications ecosystem. While the government maintains that this move is essential to bolster its blockchain-based anti-spam enforcement infrastructure, industry leaders—most notably the Swedish giant Truecaller—have decried the mandate as an "anti-competitive" measure that threatens to compromise proprietary data.
The Mandate: Integrating Apps into the National Spam Shield
The latest amendments to the Telecom Commercial Communications Customer Preference Regulations (TCCCPR) require third-party call-management applications to synchronize their spam-flagging data with the Digital Ledger Technology (DLT) platform managed by telecom service providers (TSPs).
For years, India has struggled to control the proliferation of unsolicited commercial communications. By creating a unified flow of information, TRAI intends to empower telecom operators to take swifter, more effective action against spammers. Under the new regime, when a user marks a call as spam on a third-party application, that report must be transmitted to the carrier-managed blockchain, effectively turning private app data into a public regulatory utility.
A Chronology of Conflict: Regulatory Tension in India
The friction between TRAI and the private sector is not a new development. Truecaller, which holds a dominant position in the Indian market with over 350 million active users in the country, has repeatedly found itself at odds with the regulator.
- 2025 – The Spam Surge: As India grappled with an estimated 42 billion spam calls in 2025, Truecaller emerged as the primary line of defense for millions. The company reported that it successfully blocked or identified nearly 12 billion spam calls during that year alone.
- Early 2026 – The Labeling Dispute: Tensions flared when TRAI restricted call-management apps from automatically labeling calls originating from government-designated number ranges as "spam." Truecaller argued that this exemption provided a "free pass" to unwanted callers, effectively creating a blind spot in the consumer’s spam shield.
- March 2026 – Drafting the Future: TRAI released a draft proposal suggesting the use of India’s broader IT laws to enforce stricter data-sharing requirements, signaling an intent to bring third-party apps under tighter oversight.
- July 2026 – Legal and Policy Clashes: The ongoing friction over the scope of "authorized" spam-labeling practices continued to dominate industry discussions, with Truecaller maintaining that its community-sourced data is a proprietary asset built on years of user trust.
- Late 2026 – Current Developments: The latest amendments have finalized the requirement for data sharing, further deepening the divide between the regulator’s desire for a centralized "source of truth" and the private sector’s desire for data sovereignty.
Supporting Data: The Scale of the Problem
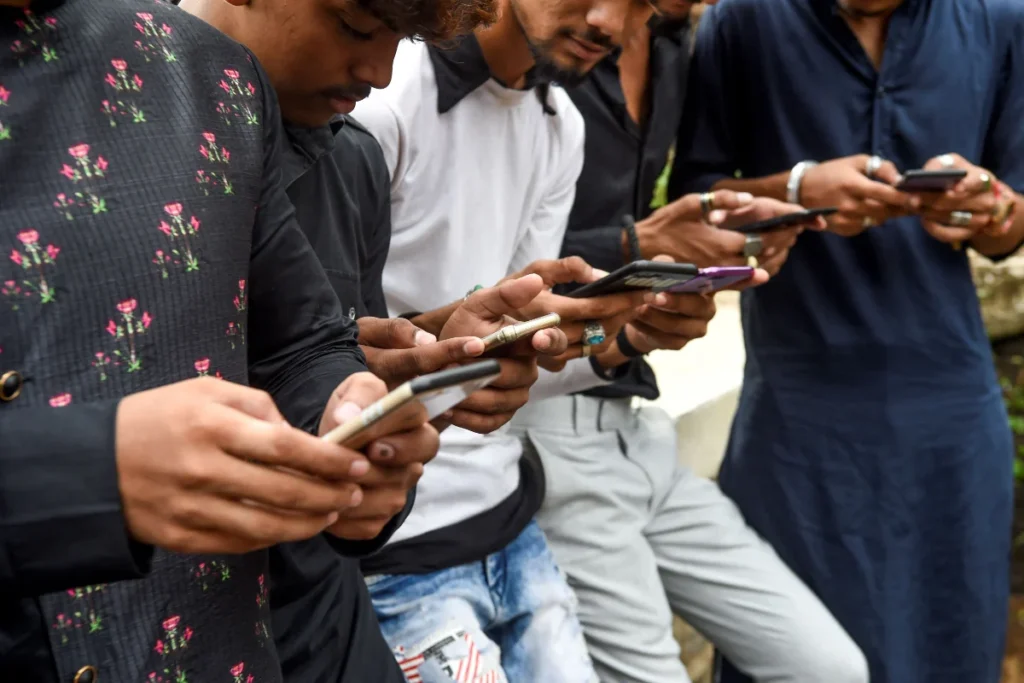
The necessity of these regulations is underscored by the sheer scale of the telecommunications landscape in India. With over a billion mobile subscribers, the country has become a massive target for automated scams, robocalls, and high-pressure telemarketing.
Truecaller’s own data reveals that the average Indian user is subjected to a staggering frequency of unwanted contact. The decision by TRAI to bridge the gap between "over-the-top" (OTT) apps and the underlying telecom network is a strategic attempt to leverage the "community wisdom" that companies like Truecaller have aggregated. However, the technical challenge remains: the regulator is attempting to integrate two distinct layers—the telecom operator’s network infrastructure and the app developer’s software layer—which were never designed to share granular, real-time user-behavioral data.
The Case for "Anti-Competitive" Practices
Truecaller has been vocal in its opposition, characterizing the mandate as a "one-way exchange." From the company’s perspective, the requirement to share spam reports—data points that are the result of significant R&D and community-driven verification—constitutes a forced transfer of commercially valuable intellectual property to the telecom operators, who are, in some cases, competitors in the caller-ID and call-management space.
"It is a fundamental concern regarding data ownership and the competitive landscape," noted a spokesperson for the company. "By forcing us to feed our intelligence into the operator’s infrastructure, we are effectively being forced to weaken our own unique value proposition while providing free, actionable data to entities that do not share the same technical burden of curating that data."
Implications: Privacy, Jurisdiction, and Technical Uncertainty
The move has prompted widespread debate among policy experts regarding the long-term implications for the Indian digital economy.
The Jurisdictional Question
Sumeysh Srivastava, a partner at The Quantum Hub, notes that this creates a complex legal ambiguity. "We are looking at a scenario where apps that are not telecom operators are being subjected to telecom-level reporting standards," he explains. "The enforcement mechanism remains murky. Will the regulator use the IT Act? Will they use the Telecom Act? The lack of clarity on the legal framework under which these apps will be held accountable creates a high degree of regulatory risk."
The "Consent" Conundrum
Kazim Rizvi, founding director of The Dialogue, raises concerns about the privacy of the end user. "If an app is required to transmit a specific user’s report to the operator, how is that user’s consent managed?" he asks. "There is a massive difference between an app identifying a call as spam for the user’s personal safety and an app being legally compelled to report that user’s personal activity to a centralized government-led database."
Rizvi emphasizes that without strict definitions of what constitutes "spam data"—whether it refers to a simple "block" command or the entire backend reputation signal—the mandate could lead to significant data privacy breaches.
New Rules for the AI Era: Addressing A2P Communications
Perhaps the most forward-looking aspect of the new rules is the regulation of AI-powered calling. TRAI has redefined "Application-to-Person" (A2P) calls to include any communication generated by software, AI voice agents, or pre-recorded scripts.
- Mandatory Disclosure: Businesses utilizing AI voice agents must now declare their use to telecom operators in advance. Any call that uses an artificial voice but fails to declare its status will be automatically flagged as spam.
- Financial Disincentives: Telecom operators are now authorized to levy a termination charge of up to 5 paise per minute on A2P calls. While this is intended to curb spam, critics like Satya N. Gupta warn that it may disproportionately affect legitimate businesses, such as contact centers and click-to-call service providers.
- The "Human-Initiated" Grey Area: The regulation creates a critical ambiguity: does a call made by a human using AI-assisted software count as A2P? Industry observers argue that without a clear distinction, the new rules could inadvertently hamper legitimate customer service operations, turning them into targets for the new anti-spam enforcement machinery.
Conclusion: A Regulatory Balancing Act
The Indian government is clearly signaling that it has run out of patience with the "wild west" nature of spam calls. By bringing third-party apps into the regulatory fold and setting strict standards for AI-generated voice communications, TRAI is attempting to build a centralized, state-enforced spam shield.
However, the cost of this ambition may be the erosion of trust between the regulator and the innovative tech firms that have, until now, provided the most effective tools for protecting Indian citizens from digital harassment. As the industry awaits further clarification on the technical standards for data transmission and the exact scope of the A2P definitions, one thing is certain: the landscape of digital communication in India is undergoing its most significant transformation in a decade. Whether this leads to a cleaner, more secure network or a stifled, over-regulated digital environment remains to be seen.